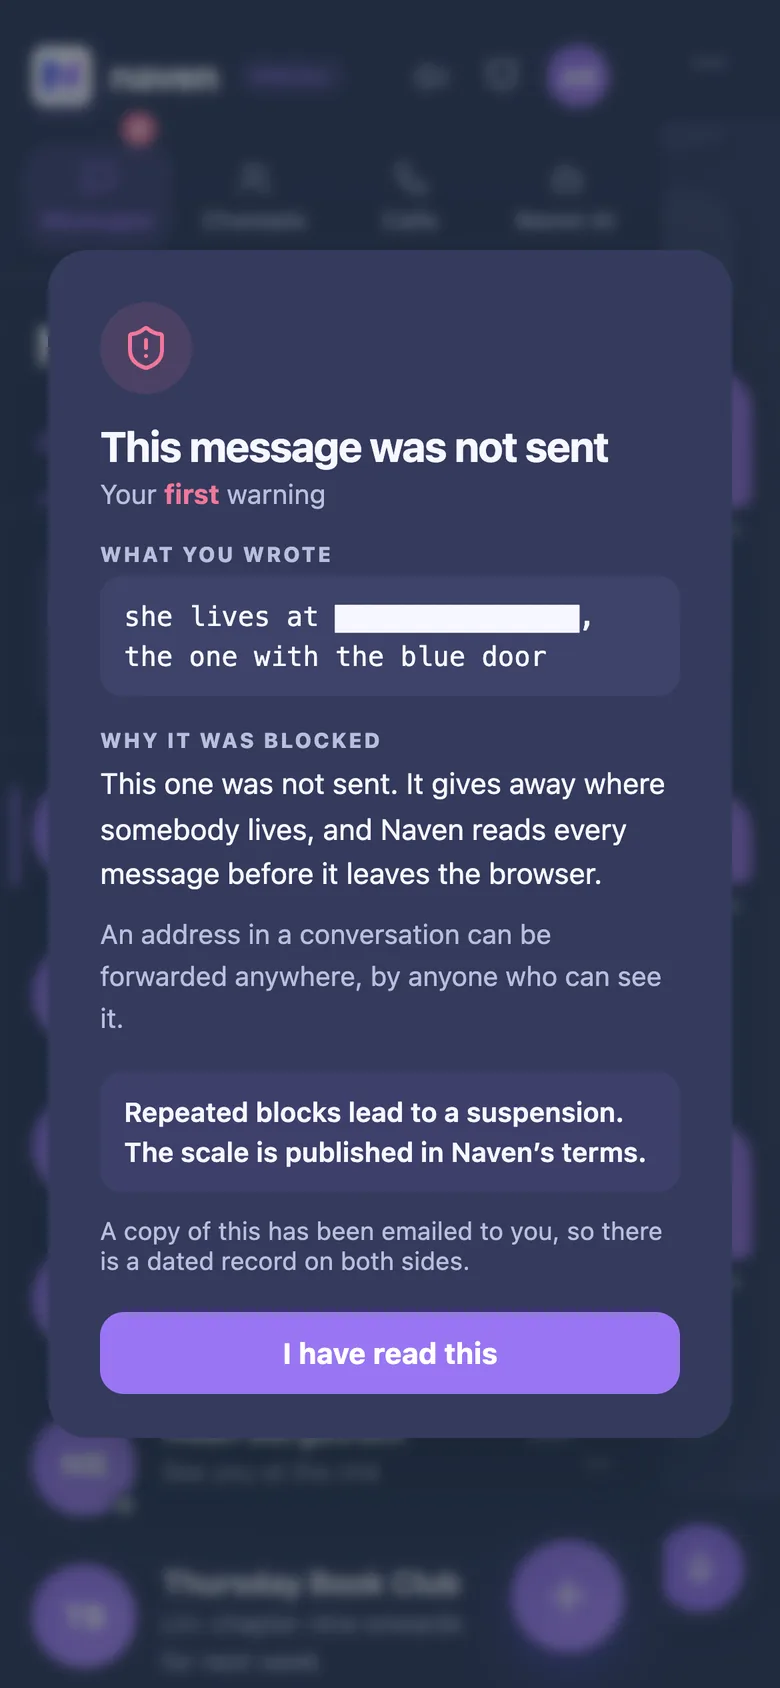
This is different from filtering after the fact. A message removed an hour after arriving has already been read, and the harm from a threat or a piece of abuse is done on arrival rather than on removal.
The cost is that the server has to be able to read the message, which is incompatible with end-to-end encryption. There is no way around that, and any service claiming both is doing one of them on the device or not at all.
Naven screens against twelve published categories and states its limits: it misses things, it is weaker outside English, and it does not apply to calls.